

AI Governance
AI inventory, usage signals, and risk tracking - aligned to ISO 42001 and fed by cloud and GitHub integrations.
Where it lives
Sidebar → AI Governance (/ai-governance)
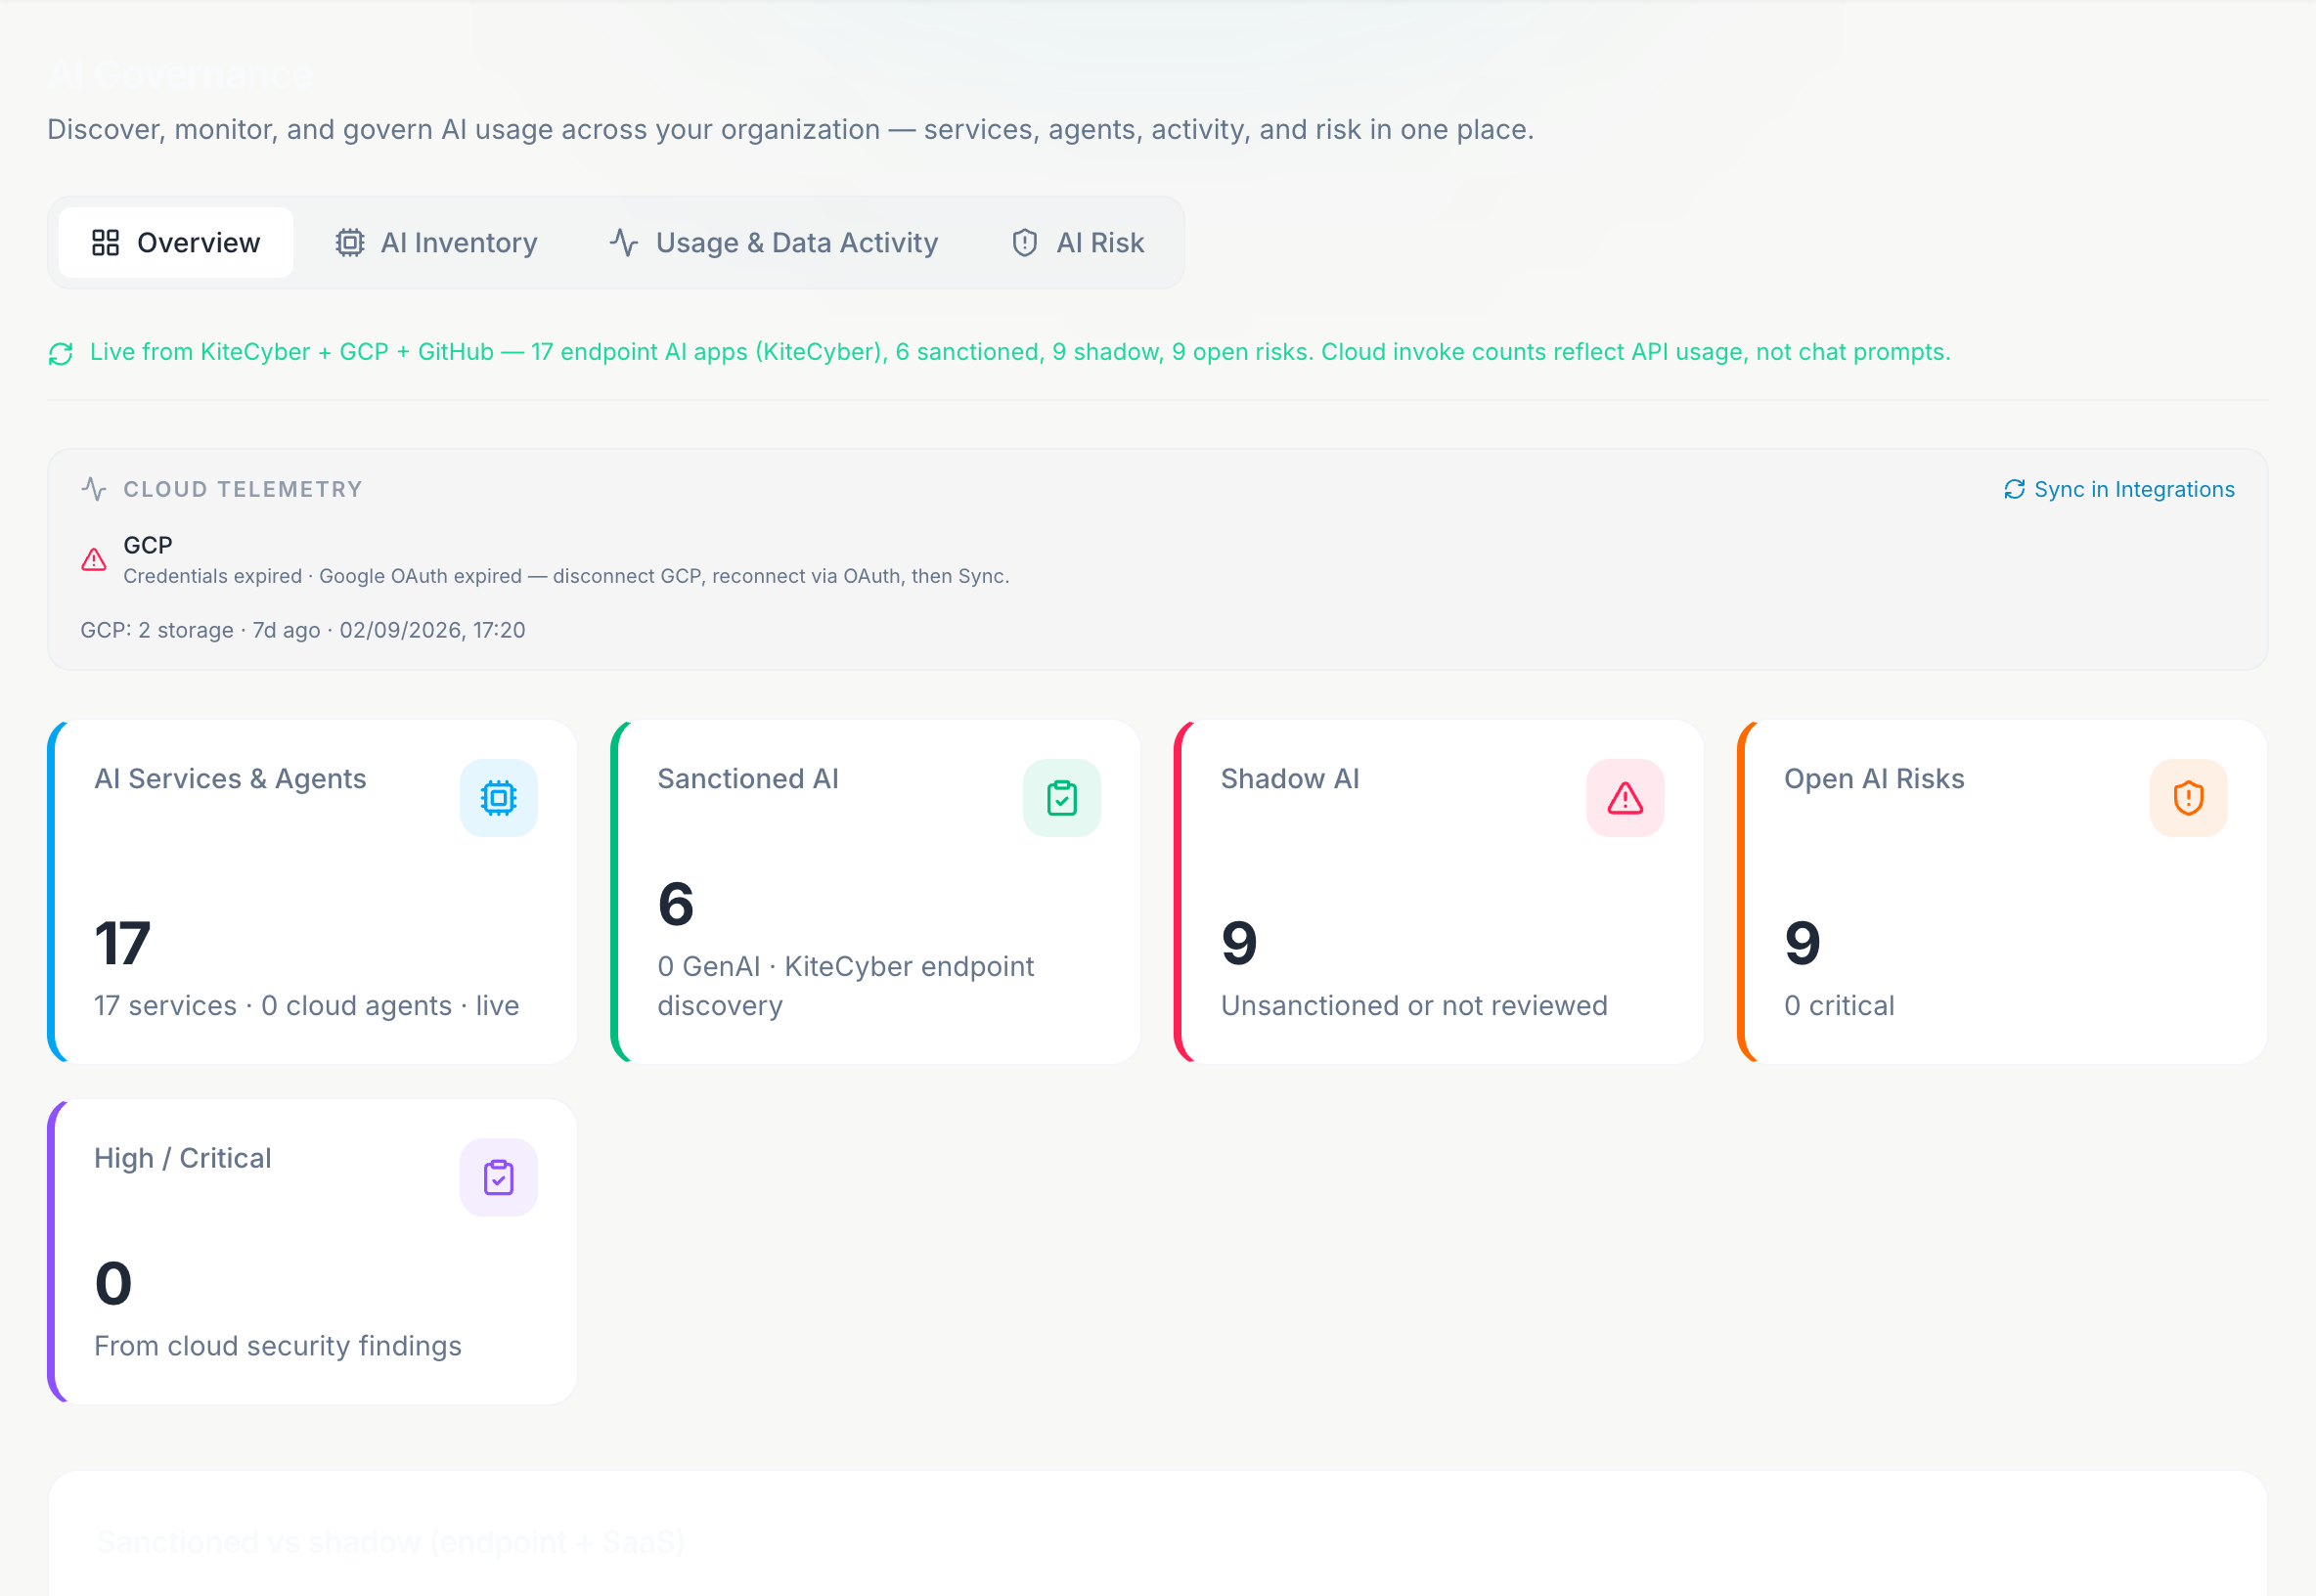
AI Governance gives security and compliance teams a single place to see what AI is in use, who is using it, and what risks need review - without replacing your framework workspace for ISO 42001.
In-page sections
Navigate with the AI Governance sub-menu:
KPI cards: total AI systems, approved vs pending, open risk issues, and connector status. Start here for a weekly AI posture check.
Catalog of AI services and applications - ChatGPT, Copilot, Bedrock, Vertex/Gemini, shadow tools, and more. Each row shows approval status, risk level, data classification, and source badges (KiteCyber, AWS, GCP, GitHub).
Usage trends and data-handling signals from connected cloud and endpoint sources. Useful for ISO 42001 A.9 and privacy reviews.
Open issues by category (shadow AI, unsanctioned Copilot, exposed API keys, missing review). Link issues to tasks and evidence in the ISO 42001 framework workspace.
Data sources
| Integration | What it feeds |
|---|---|
| KiteCyber | Endpoint GenAI apps, shadow SaaS, sanctioned vs unsanctioned tools |
| AWS | Bedrock, SageMaker, and related AI service inventory |
| Google Cloud | Vertex AI / Gemini usage and project inventory |
| GitHub | Copilot seat inventory, secret scanning alerts for AI-related keys |
Connect sources in Integrations, then sync. Until then, Atlas shows sample data with a link to Integrations.
Approval workflow
Each AI system has an approval status:
| Status | Meaning |
|---|---|
| Approved | Reviewed and allowed for use |
| Pending Review | Discovered but not yet assessed |
| Not Reviewed | New or unclassified |
| Blocked | Explicitly disallowed |
Admins update status and risk level as part of your AI governance program. Changes appear in ISO 42001 evidence when mapped.
Connect integrations
At minimum, connect the source that knows about AI in your environment (KiteCyber, AWS, GCP, or GitHub).
Review inventory
Open AI Inventory. Sort by Not Reviewed or Pending Review first.
Triage risks
Open AI Risk and assign owners or create tasks for high-severity issues.
Map to ISO 42001
Use the ISO 42001 framework workspace for controls, policies, evidence, and audit-ready snapshots.
GitHub Copilot seats discovered via the GitHub integration appear here even when endpoint agents do not see Copilot installed locally.
AI Governance complements - does not replace - the full ISO 42001 framework tabs (Criteria, Controls, Policies, Evidence, Tasks, Roadmap).