

Frameworks
SOC 2, ISO 27001, GDPR, DPDP, ISO 9001, ISO 42001, and coming-soon standards - each with a full compliance workspace.
Where it lives
Sidebar → Compliance → Frameworks (/frameworks)
Active frameworks
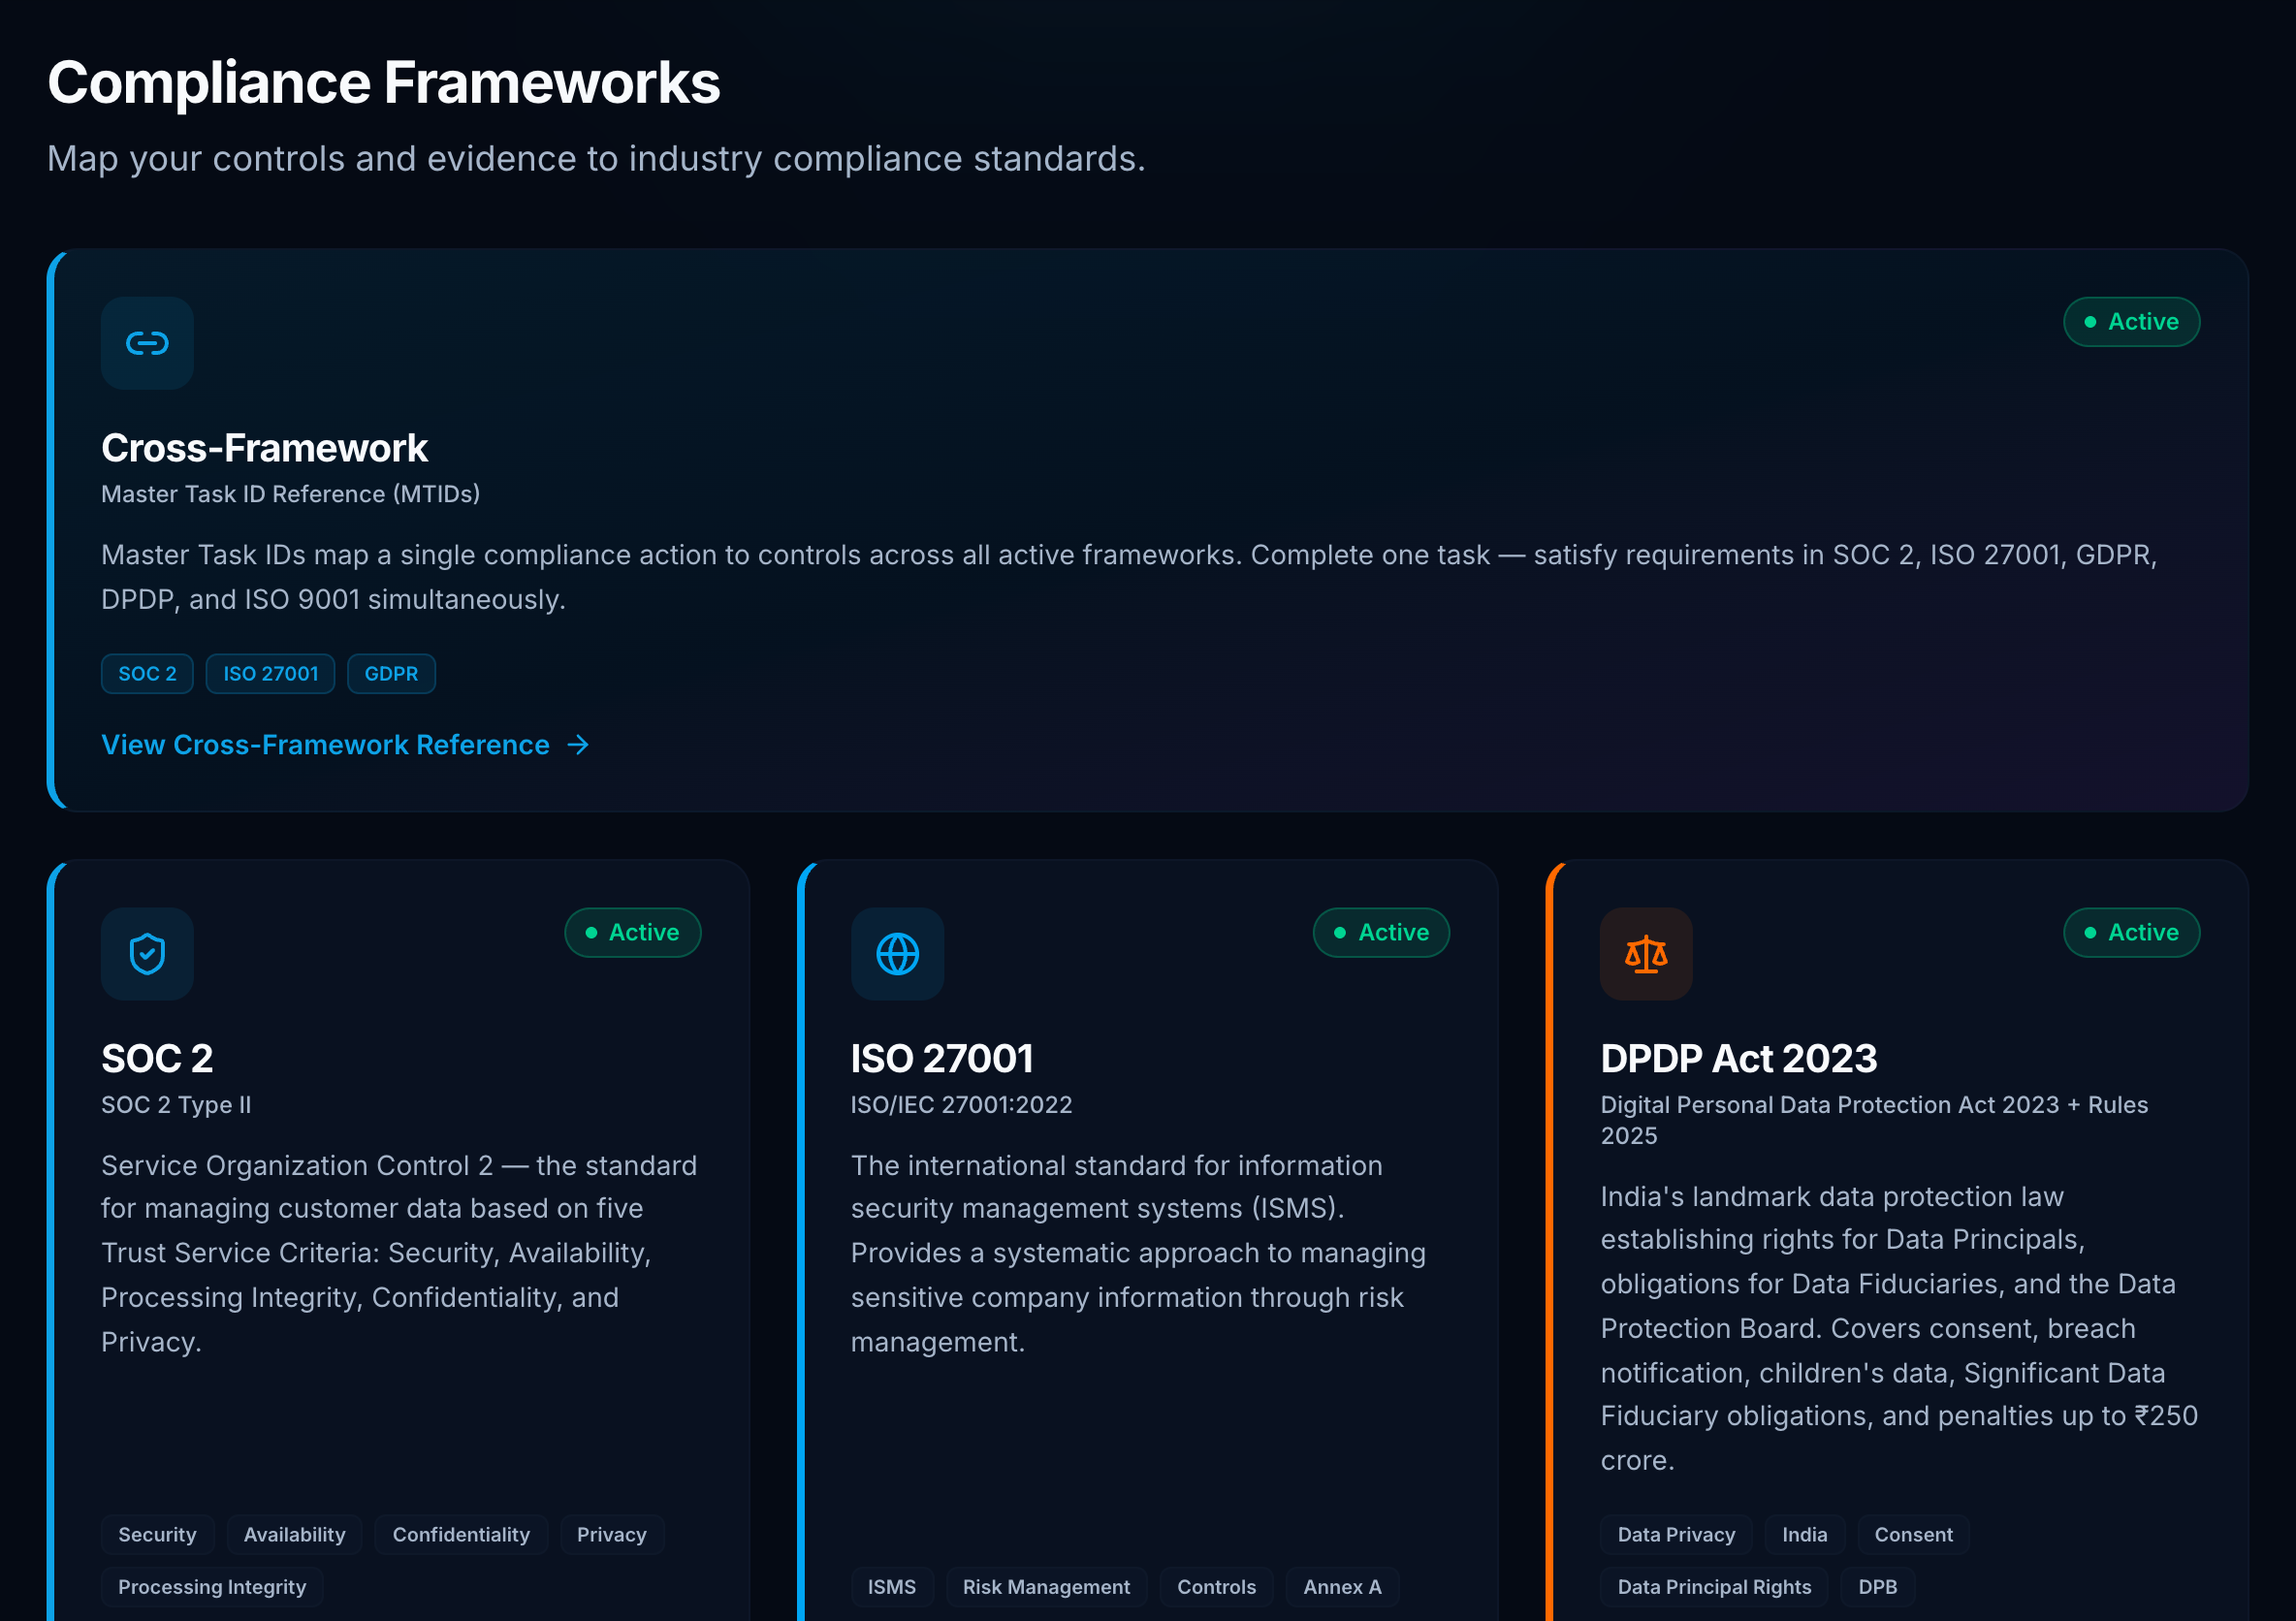
Each active framework opens a dedicated workspace with the same tab pattern:
Overview → Criteria → Controls → Policies → Evidence → Tasks → Roadmap
SOC 2
Trust Service Criteria - security, availability, confidentiality.
ISO 27001
Annex A controls and ISMS evidence.
GDPR
EU data protection articles and processing records.
DPDP Act 2023
India Digital Personal Data Protection obligations.
ISO 9001
Quality management system criteria.
ISO 42001
AI management system - pairs with AI Governance.
CIS Controls
CIS CSC v8 alignment lives at /frameworks/cis and is driven by your Assessment answers.
Cross-framework work
Cross-Framework Reference shows master tasks (MTIDs) shared across standards - implement once, satisfy multiple frameworks.
Coming soon
| Framework | Status |
|---|---|
| HIPAA | Planned |
| PCI-DSS | Planned |
Pick frameworks during onboarding or toggle them anytime from the catalog. Inactive frameworks stay visible but read-only until enabled.
Policies are maintained centrally in Policies & Standards and linked into each framework workspace.